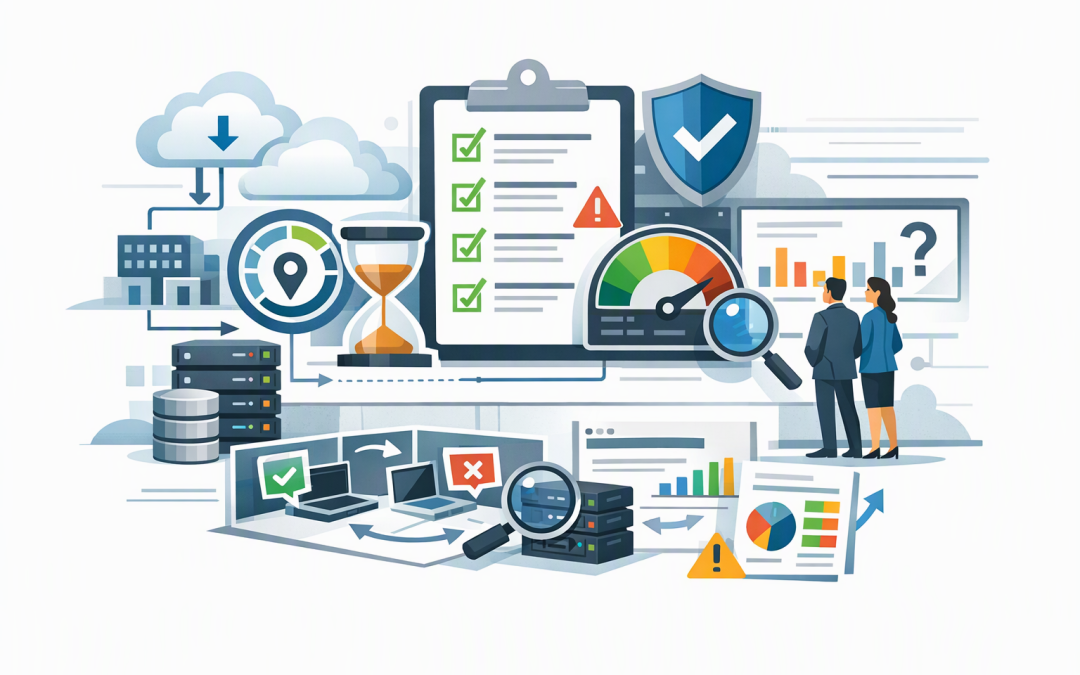
In this blog post Azure Backup Assurance Turns Inventory Into Recovery Decisions we will show how to move from a list of protected resources to recovery choices your leadership team can trust. Your Azure dashboard may look healthy, yet nobody can confidently say which systems must return first, how long recovery will take or whether the restored application will actually work.
That gap matters. A successful backup job only confirms that data was captured. Backup assurance goes further by proving that critical systems can be restored within an acceptable timeframe, by the right people, using documented steps.
What Azure Backup assurance means
Azure Backup is Microsoft’s cloud-based service for protecting virtual machines, databases, files and other workloads. Policies control how frequently backups run, how long recovery points are retained and where protected data is stored.
Depending on the workload, Azure Backup creates snapshots or application-aware copies and stores recovery points in a secure vault. A recovery point represents a version of the data that can be selected during a restore. Azure Backup focuses on protecting and restoring data, while Azure Site Recovery is used when a business needs broader disaster recovery and failover between environments.
Microsoft’s current Resiliency in Azure experience, previously called Azure Business Continuity Center, brings backup, disaster recovery and broader resilience information into one management view. Azure Resource Graph can then query protection information across multiple subscriptions, while Azure Monitor provides alerts and longer-term reporting.
These tools provide the inventory. Assurance comes from connecting that technical inventory to business importance, recovery targets and completed restore tests.
Why a protection inventory is not enough
Most backup reviews begin with a question such as, “Are all our servers backed up?” It is a useful question, but it does not reveal whether the right information is protected or whether the recovery design matches business expectations.
A company may have 98 per cent of its Azure virtual machines protected and still face serious risk. The missing two per cent could include the server that processes customer orders or an identity service required by every employee.
Even protected systems can have hidden problems. A recovery point may be too old, the retention period may not satisfy a contractual requirement, or the application may depend on another system that is restored several hours later.
The better question is, “Can we recover the business services we depend on, in the right order, within the time the business can tolerate?”
Turn the inventory into five recovery decisions
1. Decide what is genuinely business-critical
Start by grouping protected resources into business services rather than reviewing individual servers. A customer portal, for example, may rely on several virtual machines, a database, storage, networking, identity and third-party connections.
Assign an accountable business owner to each service. That owner should confirm the financial, operational and customer impact if the service is unavailable.
This prevents IT teams from spending heavily on rapid recovery for low-value systems while a critical process receives only basic protection.
2. Set recovery time and data-loss limits
Each important service needs two plain-English targets. The recovery time objective is how quickly the service must be working again. The recovery point objective is how much recent data the business can afford to lose.
A payroll archive may tolerate a 24-hour recovery time. An online ordering system may need to return within two hours and lose no more than 15 minutes of transactions.
These targets determine backup frequency, retention, storage design and whether backup alone is sufficient. Systems with very short recovery targets may also require high availability or replication. Our guide to designing zone-resilient Azure SQL Managed Instance workloads explains where availability design fits alongside backup.
3. Identify protection gaps at scale
Azure Resource Graph provides a practical way to search backup information across subscriptions rather than opening every vault manually. The following starting query lists protected items recorded through Recovery Services vaults and newer Backup vaults:
RecoveryServicesResources
| where type in~ (
 'microsoft.recoveryservices/vaults/backupfabrics/protectioncontainers/protecteditems',
 'microsoft.dataprotection/backupvaults/backupinstances'
)
| project subscriptionId, resourceGroup, type, name, properties
The output still needs business context. Add ownership, service criticality, required recovery time, last successful backup, retention policy and last restore-test date to create a useful assurance register.
Resource Graph holds recent backup and restore job information, while longer-term evidence can be retained in Azure Monitor Logs and displayed through Azure Workbooks. Microsoft’s backup reports can also show job history, policy adherence, storage usage and restore activity.
4. Test the recovery outcome, not just the restore button
A meaningful test restores the workload into an isolated environment where it cannot interfere with production. The technical team then checks the operating system, data, network access, identity permissions and required security controls.
The application owner must also confirm that the service works. Can users sign in? Are recent orders present? Can reports run? Can the system exchange data with its dependencies?
Record the total time from declaring the test to business validation. If the target was four hours but recovery took seven, the organisation has learned something valuable before a real incident.
For ransomware scenarios, the test should also confirm that recovery points cannot be easily altered or deleted by a compromised administrator. We cover that design in more depth in Immutable Azure SQL Backups for Practical Ransomware Recovery.
5. Give leaders a decision-ready scorecard
CIOs and business owners do not need a spreadsheet containing thousands of backup jobs. They need a short scorecard showing whether critical services are recoverable.
- Percentage of critical services with current backup protection
- Percentage tested within the agreed schedule
- Services that met their recovery time and data-loss targets
- Failed jobs or security alerts awaiting action
- Recovery risks requiring funding or an accepted business decision
This changes the conversation from “backup is green” to “nine of our ten critical services met their targets, and one requires a decision about additional replication.”
A practical scenario
Consider a 200-person distributor with around 60 protected Azure workloads. Its backup report appears healthy, with only a handful of failed jobs during the previous month.
When the workloads are mapped to business services, the company discovers that its ordering platform depends on an identity component excluded from the recovery plan. A restore test also takes six hours because database access, network rules and application credentials must be rebuilt manually.
The business had assumed a two-hour recovery. The assurance exercise exposes the gap and gives leadership three clear choices: automate more of the recovery, invest in replication, or formally accept the longer outage.
It also finds several non-critical development systems using expensive retention settings. Adjusting those policies helps fund the improvements without increasing the overall backup budget. For more opportunities like this, see how to lower Azure backup and recovery costs without more risk.
Support Essential 8 with evidence
Regular backups are part of the Essential Eight, the Australian government’s cybersecurity framework for reducing common cyber risks. The Australian Cyber Security Centre also expects organisations to test restoration as part of disaster recovery exercises rather than waiting for a major incident.
An assurance register creates practical evidence: what is protected, which policy applies, who owns the service, when recovery was tested, what happened and which improvements were approved.
This evidence is more useful during an assessment, customer review or cyber insurance renewal than screenshots showing that backup jobs happened to be green on one particular day.
Make recovery a tested business capability
Azure Backup provides strong protection technology, but technology alone cannot decide which service matters most or how much downtime your business can absorb. Those decisions require input from IT, security, operations and business owners.
CloudProInc combines more than 20 years of enterprise IT experience with hands-on Azure and cybersecurity work. As a Microsoft Partner and Wiz Security Integrator, our Melbourne-based team helps organisations across Australia and internationally connect Azure Backup, Microsoft Defender, Wiz and Essential 8 requirements into a practical recovery approach.
If you are not sure whether your current Azure protection inventory would translate into a successful recovery, we are happy to review it with you and identify the decisions that still need to be made — no strings attached.