In this blog post Why Shadow Agents Are Growing Faster Than Traditional Shadow IT we will explain why unauthorised AI agents are appearing so quickly, how they differ from ordinary shadow IT, and what technology leaders can do before hidden automation becomes a business risk.
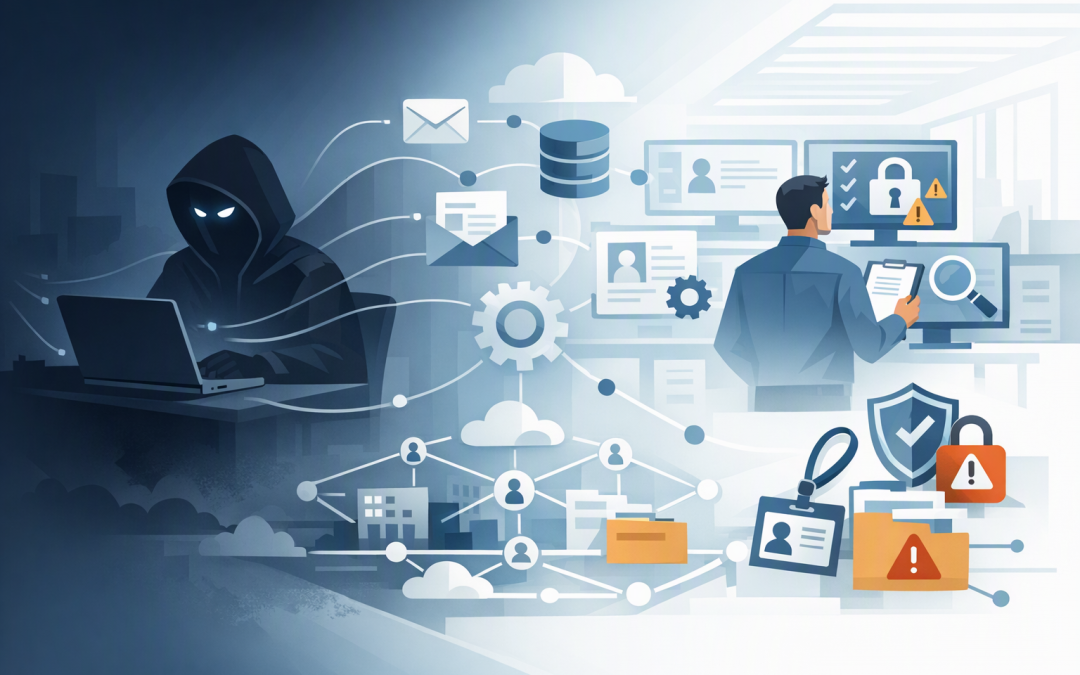
You may already have employees using AI tools without approval. The bigger concern is that some of those tools are no longer waiting for a person to type the next prompt. They can monitor inboxes, read documents, update business systems, contact customers and run scheduled tasks in the background.
What is a shadow agent?
A shadow agent is an AI-powered workflow created or connected without formal approval from IT, security or the person responsible for the business process. It may have been built by an employee, a developer, a department or even enabled as a new feature inside software the company already uses.
This extends the shadow AI problem. With shadow AI, an employee might paste information into an unapproved chatbot. A shadow agent can repeatedly access information and take action, sometimes while nobody is watching.
Most shadow agents are not created with bad intentions. They usually begin because someone wants to remove a frustrating manual task, respond to customers faster or avoid waiting weeks for an internal technology project.
How the technology works in plain English
An AI agent is more than a chatbot. It combines an AI model, such as OpenAI or Anthropic Claude, with instructions, business information and tools that allow it to perform work.
Think of the model as the agent’s brain. The instructions describe its job, while connectors act like hands that let it use Microsoft 365, customer relationship management software, finance platforms, cloud services or internal databases.
The agent also needs an identity and permissions. These determine which files, applications and records it can access. A trigger may then start the work automatically when an email arrives, a form is submitted or a scheduled time is reached.
That combination is useful, but it changes the risk. An ordinary application normally follows fixed steps. An agent can interpret information, choose between actions and continue working towards a goal. If its instructions, permissions or source information are wrong, it can make the wrong decision at machine speed.
Why shadow agents are growing so quickly
1. Building one no longer requires a development team
Employees can create useful agents through natural-language instructions and low-code tools, which let people build automation with visual menus instead of traditional programming. A technically confident operations manager can now create something in an afternoon that previously required a formal software project.
The productivity gain is real. The governance gap is that IT may not know the agent exists until it causes an error, creates an unexpected bill or accesses information it should not see.
2. Agent features are appearing inside existing software
Shadow IT traditionally involved purchasing a separate application. Agents can arrive through software that has already passed procurement, because vendors are adding AI assistants, automated actions and connectors to existing subscriptions.
This makes discovery harder. Your application list may look unchanged even though the behaviour, data access and risk inside those applications have changed significantly.
3. One agent can spread across several systems
A small workflow might begin by summarising a shared mailbox. It can quickly expand to reading customer records, drafting responses, creating support tickets and updating sales information.
Each connection increases the possible business impact. A mistake is no longer limited to one chatbot conversation; it can flow into systems used by customers, finance teams and frontline employees.
4. Agents can be copied and shared
Once one person creates a useful agent, colleagues often duplicate it for their own department. Copies may retain broad permissions, old instructions or connections established by the original owner.
This is one reason AI agent costs can scale quietly. Ten small agents may each appear inexpensive, but together they can generate substantial AI usage, cloud charges and support work.
5. Business pressure is moving faster than approval processes
Teams are being asked to reduce costs and deliver AI results now. If the approved path takes months, employees will often find their own path.
A blanket ban rarely fixes this. It usually pushes activity further out of sight. The better business response is to provide a fast, approved way to test useful ideas within clear limits.
What the risk looks like in a mid-sized business
Consider a 200-person professional services company. A team creates an agent that reads incoming client emails, checks project folders and drafts replies. To save time, it is connected using a manager’s account with access to every client folder.
The original use case works, so other teams copy it. Six months later, nobody has a complete list of the agents, several still depend on employees who have changed roles, and the business cannot easily show auditors who accessed which client information.
The problem is not simply that AI was used. The problem is missing ownership, excessive access and no reliable record of the actions taken. This is part of the wider issue we explore in how AI is expanding the attack surface, meaning the number of ways business systems and information can be exposed.
How to regain control without stopping innovation
- Find what is already operating. Review AI platforms, automation tools, cloud subscriptions, application connectors and shared accounts. Ask department leaders which workflows can read data or perform actions without a person completing every step.
- Give every agent an owner. Record its purpose, business owner, technical owner, connected systems, expected cost and review date. If nobody is accountable for an agent, it should not have access to company information.
- Give agents their own identities. Do not let important agents operate permanently through an employee’s login. A separate identity makes access easier to restrict, monitor and remove without disrupting the employee.
- Limit permissions to the task. An invoice-processing agent may need to read a particular mailbox and save files to one location. It should not automatically receive access to every finance folder or administrative setting.
- Require approval for high-impact actions. Agents can prepare a payment, customer message or account change, but a person should approve it before completion. The greater the possible financial, legal or customer impact, the stronger the approval process should be.
- Monitor behaviour, cost and lifecycle. Keep records of what agents accessed and changed. Set spending alerts, investigate unusual activity and disable agents that are no longer needed.
Where Essential Eight fits
The Essential Eight is the Australian government’s cybersecurity framework that many organisations use to reduce common security risks. Its controls around access, application management, patching and administrative privileges provide an important foundation, but they do not replace specific AI agent governance.
Businesses should extend their existing security controls to cover non-human identities, agent permissions, connected data and automated actions. Tools such as Microsoft Entra for identity, Microsoft Defender for threat protection and Wiz for cloud security visibility can help, provided they are configured around a clear governance model.
Start with visibility rather than another policy document
Shadow agents are growing faster than traditional shadow IT because they are easier to create, easier to copy and increasingly built into software employees already use. The business opportunity is significant, but so is the cost of allowing autonomous tools to operate without ownership or boundaries.
The first step is not banning agents. It is discovering them, deciding which ones deliver real value and bringing those agents into a managed environment. That creates a safer path towards the changes discussed in how AI agents will reshape enterprise IT.
CloudProInc is a Melbourne-based Microsoft Partner and Wiz Security Integrator with more than 20 years of enterprise IT experience. We take a practical, hands-on approach across Azure, Microsoft 365, OpenAI, Claude, Microsoft Defender and Wiz.
If you are not sure which agents are already operating in your business, what they can access or whether they are delivering value, we are happy to help you take a look — no strings attached.