CPI Consulting
  • Agent 365
  • Intune
  • Azure AI
  • Defender
  • Azure
  • Purview
  • Microsoft 365 Copilot
  • Blog
  • Contact Us
  • About
Select Page
Defender XDR Can Now Auto-Isolate Compromised Devices

Defender XDR Can Now Auto-Isolate Compromised Devices

by CPI Staff | Oct 12, 2026 | AI for Business & AI Strategy, AI Governance & Risk Management, Blog, C#

When a device is compromised, every minute matters. For many Australian organisations, the hardest part of incident response is not detecting that something is wrong. It is acting quickly enough to stop the attack spreading while still keeping enough visibility to...

How to Reduce Phishing Risk with Microsoft 365 Defender

by CPI Staff | Oct 12, 2026 | Blog

How to Reduce Phishing Risk with Microsoft 365 Defender

How to Reduce Phishing Risk with Microsoft 365 Defender

by CPI Staff | Oct 12, 2026 | Blog, Cybersecurity, Microsoft 365

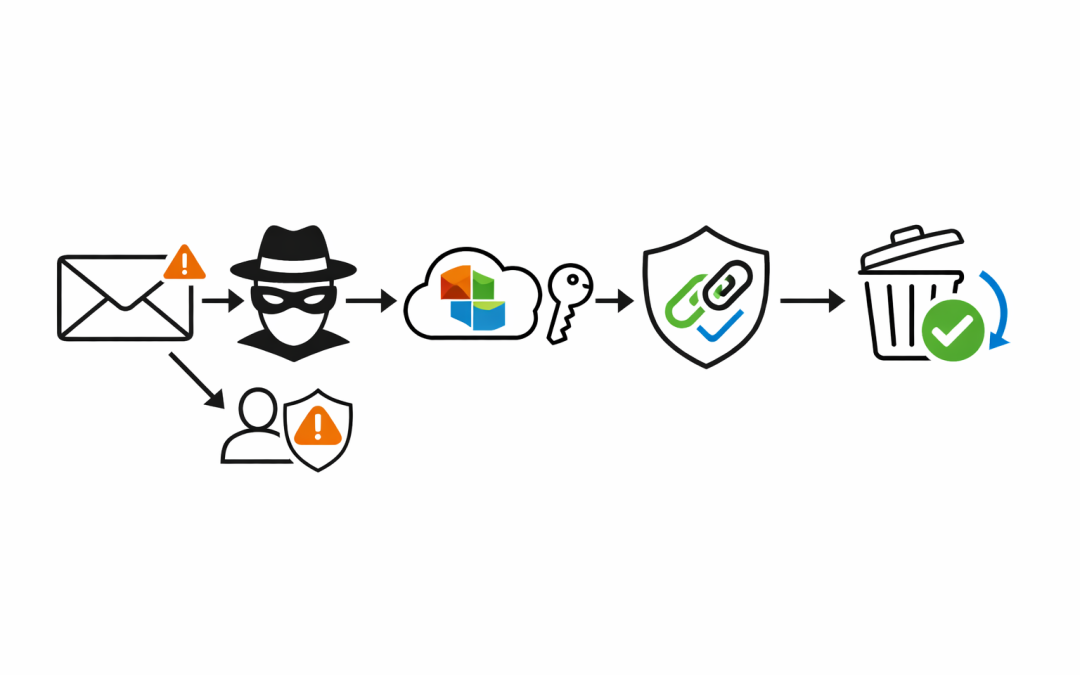
Most phishing discussions still focus on user awareness. That matters, but it is not enough. The real issue for most Australian businesses is that phishing is no longer just a bad email with poor spelling. It is impersonation, credential theft, malicious links that...
Azure Foundry Prompt Agents Vs Hosted Agents

Azure Foundry Prompt Agents Vs Hosted Agents

by CPI Staff | Oct 12, 2026 | AI for Business & AI Strategy, AI Governance & Risk Management, AI Vendor Selection & Implementation, Blog

AI agents are moving quickly from proof-of-concept demos into real business workflows. For Australian organisations, the question is no longer whether agents are interesting. The question is how to build them in a way that is secure, supportable, cost-aware, and...
Connecting Microsoft Foundry Agents to Business Systems

Connecting Microsoft Foundry Agents to Business Systems

by CPI Staff | Oct 12, 2026 | AI for Business & AI Strategy, AI Governance & Risk Management, Blog, C#

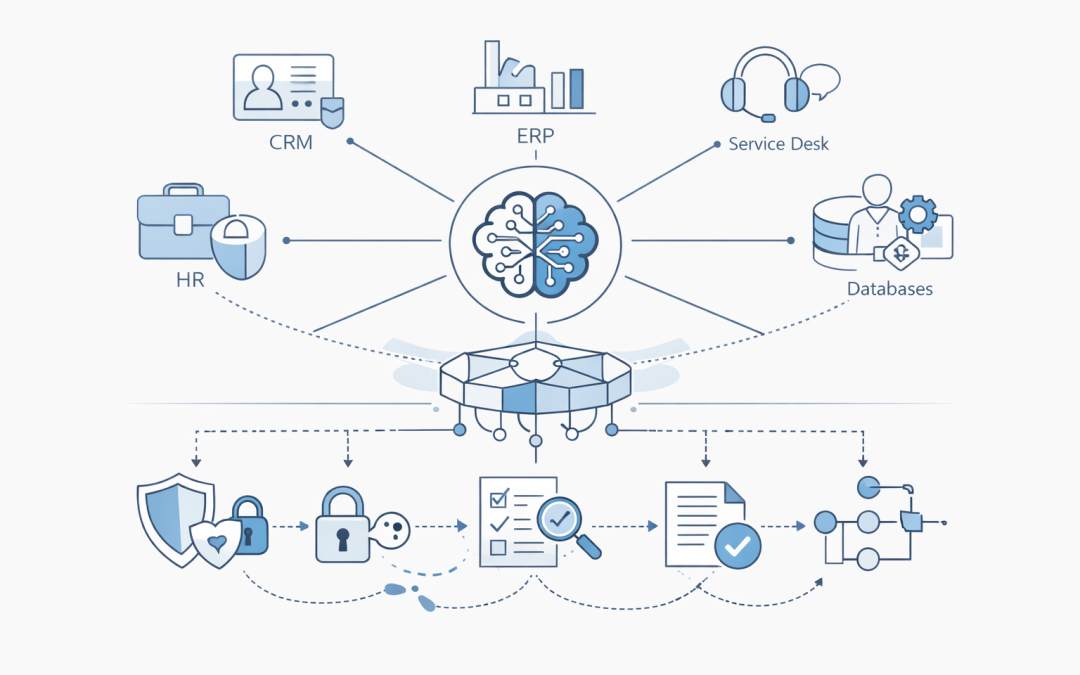
AI agents are moving from proof of concept to production planning. For many Australian organisations, the question is no longer whether an agent can answer a question. The harder question is whether it can safely do useful work across the systems the business already...
The Defender Alerts Nobody Looked At — Until It Was Too Late

The Defender Alerts Nobody Looked At — Until It Was Too Late

by CPI Staff | Oct 12, 2026 | Blog, Cybersecurity, Essential 8, Microsoft 365 Security, Microsoft defender XDR

Most security incidents do not begin with a total lack of telemetry. They begin with a signal that was already there, sitting in a queue, waiting for someone to decide whether it mattered. That is the uncomfortable reality for many Microsoft 365 environments....
« Older Entries
Next Entries »

Recent Posts

  • Find Orphaned Copilot Studio and Power Platform Assets Early
  • Securing Agentic AI and MCP Servers in Microsoft Environments
  • Azure VNet Flow Log Filtering Cuts Costs Without Blind Spots
  • Immutable Azure Backups for Ransomware Resilience and Recovery
  • Defender Move to Quarantine Speeds Up Email Threat Containment
  • Production-Ready AI Agents on Microsoft Agent Framework in Australia
  • What Microsoft Agent Framework 1.x Means for Your AI Roadmap
  • Patching Brotli CVE-2026-111497 Safely with Azure WAF Controls
  • Safe GitHub Copilot Adoption in Microsoft Teams for IT Leaders
  • How the Azure OpenAI Decisions API Cuts Agent Cost and Delay

Categories

Subscribe

Top Posts

How to Add a Registry Key to Windows 11 Using Microsoft Intune
Updating Microsoft Edge Using Intune
How to Turn Off Windows Hello in Microsoft Intune
Sync SharePoint Site Libraries with Microsoft Intune
How to Deploy a Wiz Outpost to Microsoft Azure
Setting Google Chrome as the Default Browser with Microsoft Intune
Whitelist USB Devices on Windows Using Intune
Create a Custom Extension Attribute Entra ID
Maximizing Security: When to Use Wiz Outpost with Azure
Block Copy Paste from iOS Business Apps with Intune