
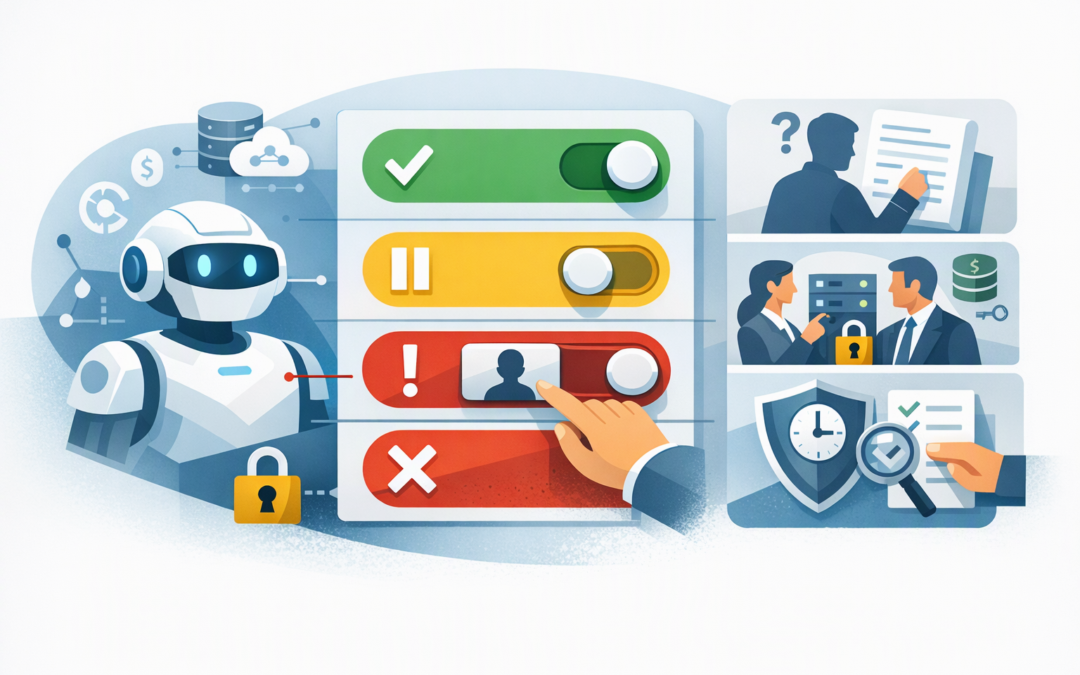
In this blog post MCP Tool Approval Policies Every Australian CIO Should Adopt we will explain how to control what AI agents can do, which actions should require human approval, and how to introduce practical governance without slowing your business down.
The risk is easy to underestimate. An AI assistant that only answers questions is relatively contained. An AI agent that can access Microsoft 365, update customer records, create accounts, change cloud resources or trigger payments can cause real damage if its permissions and approval rules are poorly designed.
What MCP tool approval actually means
Model Context Protocol, or MCP, is a standard way for AI agents to connect to business tools and data. Think of it as a common connector that lets an agent ask an approved system to perform a specific task.
Microsoft Agent Framework provides building blocks for creating AI agents and multi-step workflows using technologies such as Azure OpenAI. An agent is AI software that can interpret a request, decide which tool it needs and take an action rather than simply generating text.
CPI Consulting helps organisations design, build and secure Azure AI solutions, from Azure OpenAI and Microsoft Foundry to agents, governance and production deployment.
Visit CPI ConsultingAn MCP server publishes a catalogue of available tools. These might include tools for reading a support ticket, updating a sales opportunity, creating a Microsoft 365 user or restarting an Azure service.
A tool approval policy decides whether the requested action can run automatically, must pause for human review or must be blocked completely. This approval happens before the tool performs the action, not after the damage has already been done.
Our earlier guide on keeping Microsoft AI agent tools safe with MCP approvals explains the basic control. The bigger CIO question is how to turn that feature into an organisation-wide governance model.
Why approving every action does not work
It may feel safest to require approval for every tool call. In practice, that usually creates a queue of low-risk requests that people approve without reading.
Imagine an internal service desk agent that handles hundreds of requests each week. Requiring an IT manager to approve every search for a device record would remove most of the productivity benefit and encourage rushed approvals.
The opposite approach is equally dangerous. Allowing every approved agent to perform every available action automatically can turn a misunderstood instruction, compromised account or badly designed workflow into a serious incident.
The goal is not maximum approval. It is meaningful approval at the point where an action could create a financial, security, privacy or operational impact.
Use four policy levels based on business impact
A clear classification model helps business owners, security teams and developers make consistent decisions.
1. Allow low-risk read-only actions
Read-only tools can often run automatically when they access non-sensitive information. Examples include checking whether a managed device is compliant, retrieving a public policy document or reading the status of a support ticket.
Automatic access should still be limited to the information required for the task. Read-only does not mean harmless if the tool can search payroll records, executive email or customer identity documents.
2. Apply conditional approval to routine changes
Some actions are safe only within defined limits. An agent might reset a standard user session automatically but require approval when the affected account belongs to an administrator or executive.
Other conditions can include the value of a transaction, the sensitivity of the data, the location of the user and whether the request falls outside normal business hours. This approach keeps everyday work moving while escalating unusual situations.
3. Always approve high-impact actions
Actions that change access, move money, delete information or affect production systems should normally require a named person to approve them.
- Creating or modifying administrator accounts
- Sending external messages containing sensitive information
- Deleting customer, employee or financial records
- Changing Microsoft Defender security policies
- Deploying software across company devices
- Modifying Azure production resources
- Creating payments, refunds or purchase orders
The approver should understand the business context, not simply receive a technical prompt saying that a tool wants permission to run.
4. Block prohibited actions
Some capabilities should not be available to the agent at all. A customer service agent, for example, should have no tool for disabling security monitoring or exporting an entire customer database.
Blocking the tool is safer than relying on an approval screen. This follows least privilege, meaning every agent receives only the minimum access required to do its job.
Make approval requests understandable
An approver cannot make a sound decision if the request is vague. “Approve tool execution” provides almost no useful information.
A good approval screen should clearly show:
- Which agent requested the action
- Which user or process initiated the request
- The exact tool and business system involved
- What data will be read, changed, sent or deleted
- The identity and permissions used to perform the action
- Why the agent believes the action is necessary
- The expected result and possible impact
- When the approval expires
The approved details must also remain fixed. If the target account, tool arguments or authorisation context changes while approval is pending, the original approval should be cancelled and requested again.
What the policy looks like in Microsoft Agent Framework
Microsoft Agent Framework can apply different approval modes to hosted MCP tools. The following simplified Python example allows an invoice lookup to run without approval while requiring approval before creating a payment.
from agent_framework import HostedMCPTool

finance_tools = HostedMCPTool(
 name="finance_mcp",
 url="https://your-approved-mcp-server.example/mcp",
 allowed_tools=["get_invoice", "create_payment"],
 approval_mode={
 "never_require_approval": ["get_invoice"],
 "always_require_approval": ["create_payment"]
 }
)
This is an illustrative configuration, not a complete production control. Authentication, logging, data boundaries, error handling and the permissions of the identity calling the finance system still need to be designed correctly.
Microsoft Agent Framework is developing quickly, and approval behaviour can differ between hosted tools, locally executed tools and provider-managed services. Pin tested software versions, review release notes and test rejected, expired and interrupted approvals before deployment.
For the wider technical design, see our reference architecture for securing agentic AI and MCP servers. It covers the identity, network and data controls that must sit around approval policies.
A common 200-person business scenario
Consider a 200-person organisation introducing an AI agent for employee onboarding. The agent can create Microsoft 365 accounts, assign licences, enrol devices through Microsoft Intune, which manages and secures company devices, and add employees to internal groups.
If every step requires approval, onboarding remains slow and IT gains little. If nothing requires approval, an incorrect request could give a contractor access to payroll files or administrator systems.
A balanced policy could automatically create a standard account from an approved HR record. Access to normal departmental resources could follow predefined rules, while privileged access, unusual licence costs and exceptions would require approval from the relevant system owner.
The business outcome is faster onboarding without giving the agent unlimited authority. IT staff spend time reviewing exceptions instead of repeatedly approving predictable tasks.
Connect AI governance with Essential 8 controls
The Essential 8 is the Australian Government’s cybersecurity framework for reducing common cyber risks. It does not replace a dedicated AI governance program, but several of its principles support safer agent deployment.
Application control can help restrict which software and tools may run. Limiting administrative privileges supports least-privilege agent identities. Patching applications and operating systems is relevant to Agent Framework components, MCP servers and their dependencies.
Approval records should also feed into your security monitoring. Microsoft Defender and Wiz, a cloud security platform that identifies risks across cloud environments, can help teams detect unusual identities, exposed services and unexpected activity surrounding agent infrastructure.
This gives CIOs evidence that controls are operating, rather than relying on a policy document that nobody can verify.
Five governance questions to ask before production
- Who owns each tool? Every tool needs a business owner accountable for its purpose and risk.
- What can the agent identity access? Approval cannot compensate for an identity with excessive permissions.
- Which actions fail closed? If approval services or logs are unavailable, sensitive actions should stop rather than continue.
- Can we reconstruct a decision? Logs should show the requester, approver, action, parameters, time and result.
- How quickly can access be removed? You need a practical way to disable a tool, agent or MCP server during an incident.
These controls should be reviewed whenever a tool changes. A harmless lookup tool can become high risk if a future version gains update or export capabilities.
Govern the action rather than the AI label
MCP approval policies are not just a developer setting. They are the point where an organisation decides how much authority it is willing to give an AI agent.
The strongest approach combines tool classification, least-privilege identities, understandable approval requests, reliable audit records and regular testing. This reduces security and compliance risk while preserving the productivity gains that made the agent worthwhile.
CloudProInc brings more than 20 years of enterprise IT experience as a Microsoft Partner and Wiz Security Integrator. Our Melbourne-based team helps organisations design practical controls across Azure, Microsoft 365, Defender, Intune, OpenAI, Claude and Wiz without turning AI governance into a giant consulting exercise.
If you are unsure whether your AI agents have too much access, too many approval prompts or no clear accountability, we are happy to review the setup with you — no strings attached.