
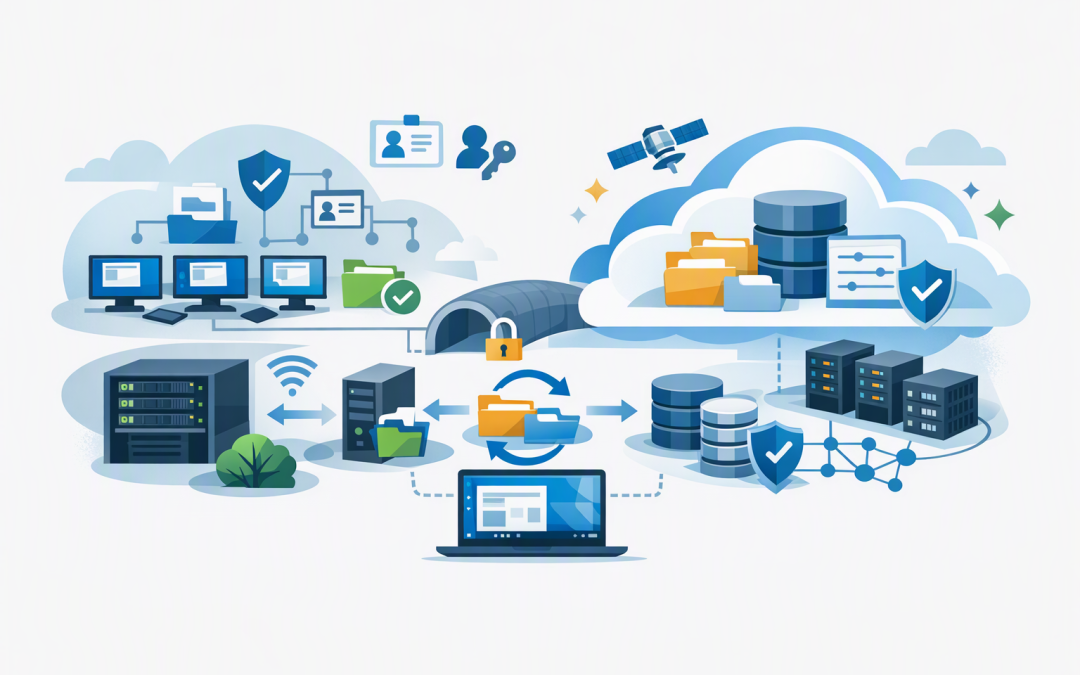
In this blog post Azure Files for AVD Hybrid Design Choices Mid-Market IT Must Make we will explain how to give employees fast, reliable access to their files without simply moving an old file-server problem into Azure.
This matters because a hybrid desktop can look successful during a small pilot, then struggle when 100 employees sign in on Monday morning. Slow profiles, unreliable file access and unexpected storage charges usually come back to design choices made before the first user was added.
What Azure Files and Azure Virtual Desktop Hybrid actually do
Azure Virtual Desktop Hybrid allows desktops and business applications to run on servers in your own office or data centre while Microsoft manages the connection and desktop service through Azure. The on-premises session hosts are registered using Azure Arc, which brings servers outside Azure into a central management platform.
Azure Files is Microsoft’s managed cloud file-sharing service. It provides familiar Windows-style shared folders without requiring your team to maintain another traditional file server in Azure.
Azure File Sync can then keep frequently used files on a local Windows Server. Employees receive local network performance, while Azure Files becomes the central cloud copy of the data.
- Azure Virtual Desktop manages how users connect to desktops and applications.
- Azure Arc connects and manages the on-premises session hosts from Azure.
- Azure Files holds the central cloud-based file share.
- Azure File Sync keeps commonly accessed data close to employees on a local server.
The concept is straightforward. The design decisions behind identity, performance, networking and recovery are where projects either become dependable business platforms or ongoing support problems.
Start with where the desktop sessions will run
File storage should normally be close to the computers using it. In an Azure Virtual Desktop Hybrid environment, those computers are the on-premises session hosts, not the laptops sitting on employees’ desks.
If every file request travels from Melbourne to an Azure region and back, small delays can accumulate. Opening documents may feel acceptable, but applications that constantly read and write small files can become noticeably slower.
Azure File Sync is useful here because a local Windows Server can serve active files at local network speed. Changes are synchronised to Azure Files over an encrypted outbound connection, generally using standard HTTPS traffic.
This also reduces dependence on a perfect internet connection. However, it does not remove that dependency completely. New files, uncached content and synchronisation still need a healthy link to Azure.
Separate user files from desktop profiles
One of the most common mistakes is putting every type of data into one large share. Department folders, employee home drives, application data and desktop profiles behave differently and should not automatically use the same storage design.
Azure Virtual Desktop commonly uses FSLogix, which stores each employee’s Windows profile in a virtual disk file. That profile includes settings and application information that must be available when the employee signs in to any session host.
Profile storage is sensitive to delay and short bursts of heavy activity. At 8:55 am the system may be quiet. At 9:00 am, dozens of profiles may open together as employees start work.
For that reason, profile containers should usually have a dedicated, performance-tested storage path. Azure Files on solid-state storage may be appropriate, but it must be tested from the actual on-premises session hosts across the real network connection.
Do not assume that a design suitable for Word documents is automatically suitable for FSLogix profiles. Separating workloads also makes troubleshooting easier and prevents a busy department share from slowing down employee sign-ins.
Choose identity before configuring storage
Employees should access files using their normal company identity. Storage account keys, which act like powerful master passwords, should not be the everyday access method.
Azure Files supports identity-based access through existing Active Directory services or Microsoft Entra Kerberos. Microsoft Entra is Microsoft’s cloud identity platform, while Kerberos is the trusted sign-in method Windows uses to confirm a user’s identity without repeatedly asking for a password.
The correct option depends on whether session hosts use traditional on-premises Active Directory, cloud identities or a mixture of both. It also depends on whether users connect to the local File Sync server, Azure Files directly or both.
Permissions must be planned at two levels. The first controls who can reach the share. The second controls which folders and files they can open, change or delete.
This is an important security boundary. A broad permission assigned for convenience can expose payroll, customer or board information to far more employees than intended.
Design networking as a business dependency
A file platform is only as reliable as the path connecting users to it. Mid-market organisations should document what happens if the primary internet service, VPN, DNS service or local cache server fails.
DNS is the service that translates a storage name into the correct network address. It sounds minor, but incorrect DNS is a frequent cause of Azure Files connections unexpectedly taking a public route or failing completely.
If session hosts access Azure Files directly, private endpoints should be considered. A private endpoint gives the storage service a private network address, allowing access through a site-to-site VPN or ExpressRoute connection rather than exposing the share through a public endpoint.
For organisations using Azure File Sync, the local server needs reliable outbound access to Azure. Monitoring should cover synchronisation health, files waiting to upload, cache capacity and connectivity failures.
Azure Arc adds another management dependency that should be included in the network plan. Our article on how Azure Arc makes hybrid disaster recovery simpler in Australia explains how Arc fits into broader hybrid recovery planning.
Size for activity rather than stored capacity
A business may have only two terabytes of employee data but still generate intense bursts of activity. Capacity tells you how much data exists. It does not tell you how quickly employees need to access it.
Storage planning should consider concurrent users, profile sizes, sign-in peaks, common applications and the number of file operations. Solid-state Azure Files generally suits performance-sensitive workloads, while lower-cost storage may suit ordinary documents and archive-style data.
Run a pilot with a realistic group, including users with large Outlook mailboxes, Teams activity, OneDrive data and line-of-business applications. A test involving five IT staff will not represent a 200-person organisation at the start of the working day.
Cost modelling should also include transactions, backups, private networking, monitoring, the local cache server and support effort. The cheapest storage tier can become the most expensive choice if employees regularly wait for files or IT spends hours investigating performance complaints.
Plan recovery before employees depend on it
Azure File Sync is not a backup. If an employee or compromised administrator deletes data, that deletion may be synchronised to the cloud and other connected locations.
Use Azure Files snapshots or Azure Backup, enable soft delete and restrict who can change backup settings. Soft delete provides a recovery window when a file share is accidentally or maliciously removed.
You should also choose storage redundancy based on the impact of an outage. Zone-redundant storage keeps copies across separate facilities within an Azure region, but the right choice depends on regional support, cost and recovery requirements.
Document how quickly files must be restored and how much recent data the business can afford to lose. Then test the recovery process rather than assuming the backup dashboard proves it will work.
This supports the Australian Essential 8, the government’s cybersecurity framework that includes regular backups, multi-factor authentication and restricted administrative access. For a wider resilience plan, see how Australian mid-market firms build stronger Azure resilience.
A practical mid-market scenario
Consider a 180-person Melbourne professional services firm with an ageing file server, several applications that must remain on-premises and employees working across two locations.
Moving every desktop and file directly into Azure could increase cost and introduce delay for the legacy applications. Keeping everything on-premises would leave the business facing another storage refresh and limited recovery options.
A balanced design could keep Azure Virtual Desktop Hybrid session hosts near the applications, use Azure File Sync for department and home-drive data, and place performance-sensitive profiles on a separate tested share. Azure Files would provide the central cloud copy, while backups, private connectivity and role-based permissions reduce recovery and security risk.
The business outcome is not simply “files in Azure”. It is avoiding a large storage replacement, improving recovery options and giving employees consistent access without slowing down their working day.
The decision is architectural, not just technical
Azure Files can remove much of the hardware maintenance associated with traditional file servers. But it will not fix unclear permissions, weak networking, oversized profiles or an untested recovery plan.
CloudProInc combines more than 20 years of enterprise IT experience with hands-on Azure, Microsoft 365, Intune, Defender and Wiz security expertise. As a Melbourne-based Microsoft Partner and Wiz Security Integrator, we focus on practical designs that fit the organisation rather than forcing every workload into the same template.
If you are considering Azure Virtual Desktop Hybrid and are unsure where profiles, shared files and backups should live, we are happy to review the proposed design before it becomes expensive to change — no strings attached.