
In this blog post Post-Quantum TLS on Azure Front Door What Leaders Should Do Now we will explain what Microsoft’s new protection actually changes, where your organisation remains exposed and how to respond without creating unnecessary cost or disruption.
The immediate problem is not that quantum computers are breaking business encryption today. It is that attackers can capture encrypted traffic now, store it and potentially decrypt it later when more powerful quantum computers become available.
That matters if your systems handle information that must remain confidential for years. Customer identities, financial records, health information, legal documents, intellectual property and sensitive government data are obvious examples.
What post-quantum TLS does in plain English
TLS is the security technology that creates the encrypted connection between a user and your website, portal or application. It is what puts the padlock in the browser and prevents someone from easily reading information while it travels across the internet.
CPI Consulting helps organisations design, build and secure Azure AI solutions, from Azure OpenAI and Microsoft Foundry to agents, governance and production deployment.
Visit CPI ConsultingBefore encrypted information can be exchanged, the user’s device and the service must agree on a temporary secret key. Future quantum computers may be able to defeat some of the mathematics currently used to establish that key.
Post-quantum cryptography uses different mathematical problems that are expected to remain difficult for both conventional and quantum computers. Azure Front Door now supports hybrid key exchange, combining a conventional method with a post-quantum method called ML-KEM.
The word “hybrid” is important. Rather than betting everything on one new technology, the connection uses both established encryption and the newer quantum-resistant approach. The session remains protected if either component remains secure.
For a broader introduction, start with our plain-English guide to post-quantum TLS on Azure Front Door. Here, we will focus on the decisions security leaders need to make next.
What Microsoft has changed
In November 2026, Microsoft made configurable TLS key exchange policies with hybrid post-quantum support generally available for Azure Front Door Standard and Premium. Azure Front Door is the service that can sit in front of public websites and applications to improve performance, route traffic and block common attacks.
Compatible devices using TLS 1.3, the latest widely used version of TLS, can now negotiate a hybrid post-quantum connection with Azure Front Door. Older or incompatible clients can continue using approved conventional methods when fallback is allowed.
Microsoft’s Standard key exchange policy is the recommended starting point for most organisations. It includes hybrid options as well as conventional options, helping businesses improve protection without immediately excluding older browsers, applications or partner systems.
Do not mistake this for complete quantum protection
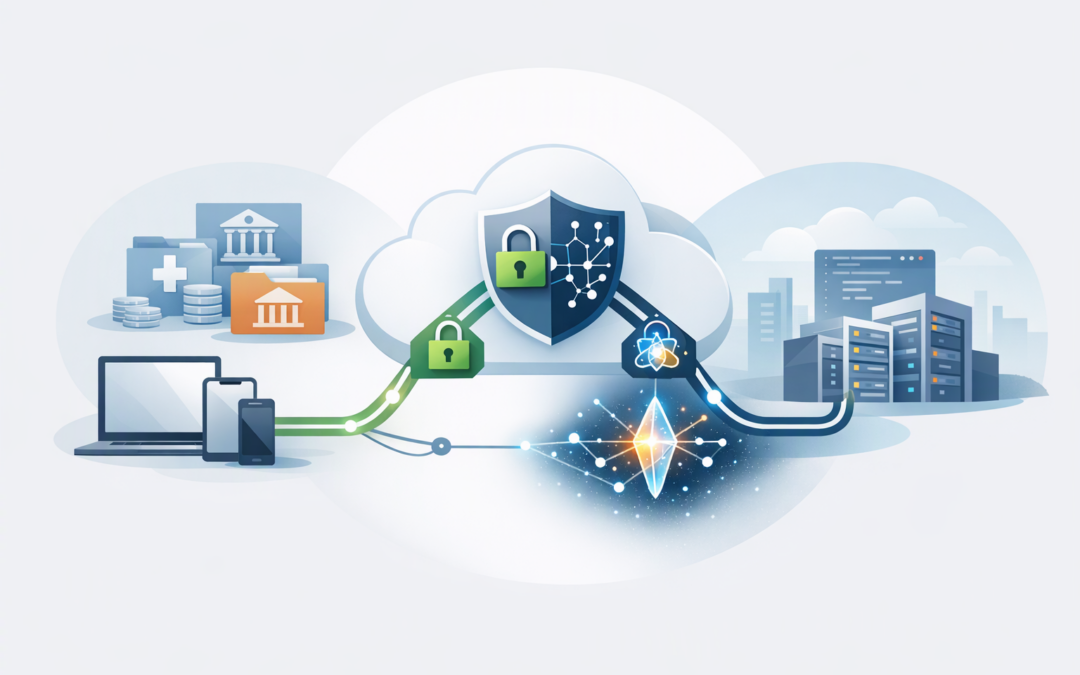
The most important limitation is that the new protection applies to the connection from the user’s device to Azure Front Door. Front Door ends that connection, inspects and routes the request, then creates a separate connection to the application behind it.
That second connection is not made post-quantum simply because the Front Door setting is enabled. Your origin systems—the web servers, application platforms and APIs processing the request—still need HTTPS, strong access controls and an independent post-quantum roadmap.
The feature also focuses on establishing the encryption key. It does not automatically make website certificates, application authentication, stored data or every internal connection quantum-resistant.
This is still a useful step. Protecting the public-facing segment reduces the amount of valuable traffic that could be collected for a “harvest now, decrypt later” attack. It just should not be reported to executives or auditors as an end-to-end solution.
Five actions Australian security leaders should take now
1. Identify which data needs long-term confidentiality
Start with the business information, not the encryption settings. Ask which data would still cause financial, legal or reputational damage if exposed five, ten or fifteen years from now.
Prioritise customer portals, payment workflows, health and identity systems, legal platforms, research environments and business-to-business APIs. A public marketing website with no sensitive transactions is usually a lower priority.
This produces a risk-based investment plan instead of an expensive attempt to change everything at once.
2. Confirm what is actually running through Azure Front Door
Many organisations do not have a reliable list of their public domains, application entry points and APIs. Shadow services, forgotten test domains and systems managed by external developers can easily be missed.
For each service, record the Azure Front Door tier, custom domain, TLS policy, key exchange policy, certificate owner, origin destination and business owner. If you are still using Azure Front Door Classic, include migration to Standard or Premium in the plan because the new key exchange controls apply to those newer tiers.
3. Begin with hybrid compatibility rather than post-quantum only
It can be tempting to select the strictest possible custom policy and declare the project finished. That approach can block older mobile devices, scanners, embedded equipment, application libraries and partner systems that do not support the required connection methods.
For most mid-market organisations, the sensible starting point is Microsoft’s Standard key exchange policy. It prefers compatible hybrid connections while retaining conventional options for clients that still need them.
Test before removing fallback. Avoiding an outage is just as important as improving encryption.
4. Test real customer and partner journeys
A successful browser test from the IT team’s laptops is not enough. Test current and older browsers, mobile applications, automated API clients, remote offices, security inspection tools and systems operated by business partners.
Pay particular attention to integrations that rely on certificates or older software libraries. If partner APIs use client certificates, our Azure Front Door mutual TLS playbook for B2B APIs explains how to strengthen identity checks without confusing them with post-quantum encryption.
Document a rollback process before making changes. The business outcome is stronger protection without interrupted sales, customer service or supply-chain operations.
5. Secure the connection behind Front Door
Require HTTPS between Azure Front Door and every origin. Where possible, prevent users and attackers from bypassing Front Door and connecting directly to the application.
Azure Front Door Premium can use Private Link, which creates a private path to supported Azure services. Other controls include restricting approved network sources, validating Front Door requests and protecting administrative access.
Private keys also deserve attention. Our guide to keyless TLS for Azure web application security explains how sensitive website keys can be kept inside protected hardware rather than copied across servers.
A practical mid-market scenario
Consider a 200-person Australian financial services company with a customer portal behind Azure Front Door. Most customers use current browsers, but one partner submits data through an older automated client and several staff use a legacy mobile application.
Moving immediately to a custom policy that permits only hybrid post-quantum methods could disconnect those systems. Doing nothing, however, leaves all customer traffic dependent on conventional key exchange.
A safer approach is to retain compatible fallback, enable the recommended hybrid policy, test every important user journey and set deadlines for upgrading the remaining applications. The company gains protection for modern clients now without causing an avoidable operational incident.
How this fits Australian security obligations
Post-quantum TLS is not currently one of the Essential Eight, the Australian government’s cybersecurity baseline covering controls such as patching, multi-factor authentication and backups. It should not replace those immediate priorities.
However, the Australian Signals Directorate recommends that organisations plan to cease using traditional asymmetric cryptography by the end of 2030. For businesses with complex applications, long supplier contracts or equipment that is difficult to upgrade, that is not far away.
Use the next contract renewal to ask cloud providers, software vendors and managed service providers for their post-quantum roadmap. Include responsibilities, supported standards, testing evidence and expected transition dates.
This work should also sit beside your wider resilience program. As discussed in our guide to building stronger Azure resilience, security changes are most effective when ownership, recovery procedures and access controls are clear.
A straightforward 90-day plan
- First 30 days: Inventory public domains, Front Door profiles, origins, sensitive data and critical client types.
- Days 31 to 60: Validate policies, select a lower-risk pilot service and test browsers, applications, APIs and security appliances.
- Days 61 to 90: Expand the rollout, address origin-side gaps and add post-quantum requirements to vendor reviews and risk reporting.
The goal is not to claim that your organisation is “quantum safe” overnight. It is to reduce high-value exposure now while building a controlled path towards broader cryptographic change.
Start with verification, not assumptions
Azure Front Door’s new capability is a valuable low-disruption step, particularly for organisations already using the service. But the business benefit depends on correct configuration, compatible clients and protection of the separate connection to your application.
CloudProInc is a Melbourne-based Microsoft Partner and Wiz Security Integrator with more than 20 years of enterprise IT experience. We take a practical, hands-on approach across Azure, Microsoft 365, Microsoft Defender, Wiz and emerging AI and security risks.
If you are unsure whether your Azure Front Door environment is receiving the protection you expect—or whether stricter settings could interrupt customers or partners—we are happy to review it with you, with no strings attached.